Security measures have evolved but have not been systematically assessed.
Solutions / 02 / Information Security & Compliance
Information security that works in everyday operations.
Understand risks. Clarify responsibility. Embed effective measures.
Security and compliance requirements need to fit your workflows. NALVRA helps assess technical risks, establish effective security structures and introduce new technologies securely.
Who we work for
For business leaders, IT managers and information security officers looking to assess and improve established security structures.
Information security strategy
Overview of the assessed situation and key gaps
Your starting point
When protection needs and measures do not align.
We help identify critical processes and systems, define responsibilities and prioritize security measures by impact and effort. Information security is an independent service, also without an AI project.
- Security measures have evolved but have not been systematically assessed.
- Responsibilities and evidence are not clearly documented.
- New technologies need a controlled introduction.
Clarity on required action
Make business-critical information, processes and dependencies visible. Assess measures by their importance to your operations.
Structured responsibility
Organize responsibilities, decisions and evidence so information security can be maintained in daily work.
Traceable implementation
Turn findings into concrete work packages and review criteria. Document progress and remaining risks clearly for responsible staff.
What we contribute
From risk to practical measures.
We tailor these building blocks to your project.
Information security strategy
We connect business goals and protection needs with actionable security planning. This includes scope, responsibilities, key dependencies and a prioritized improvement path.
ISO 27001 consulting & ISMS support
When establishing or improving an information security management system, we support processes, policies, risk assessments and evidence. Existing ways of working are considered; independent certification is a separate process.
NIS2 readiness
We help identify your starting point and potential organizational and technical gaps. Applicable requirements are assessed with the relevant specialists and translated into appropriate measures and evidence tasks.
Risk assessments & security reviews
An agreed review scope defines the systems, documents and processes covered. Findings describe the situation, possible impact, priority and recommended next steps with clear reasoning.
AI governance & AI risk management
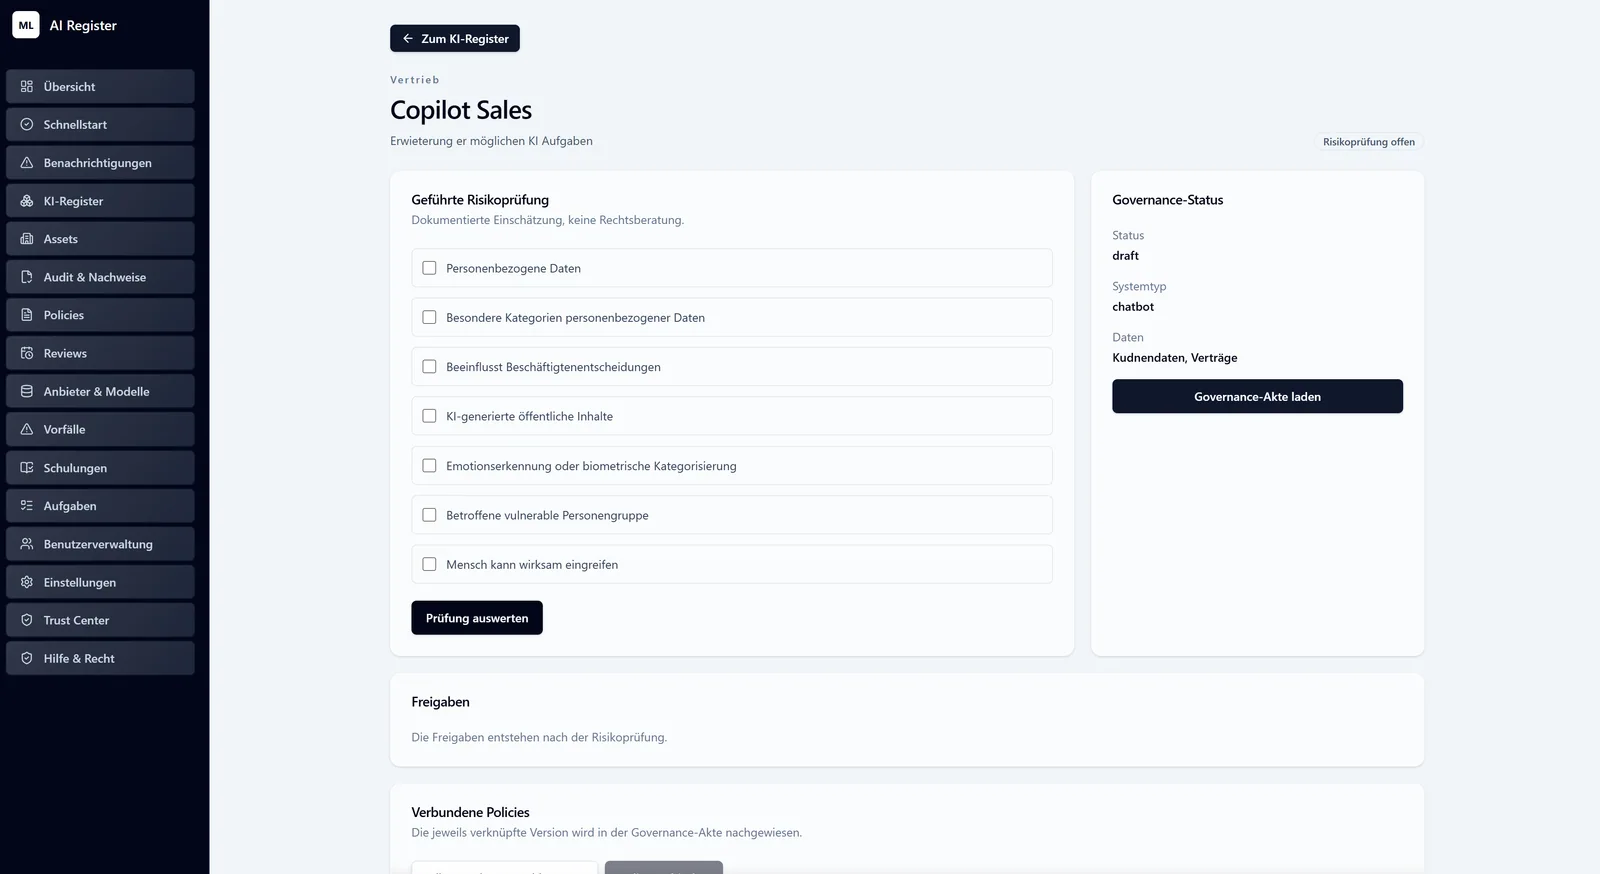
We help record AI applications, data sources, responsible staff and usage boundaries. Approvals, permitted use, human control and change handling are designed for each use case.
Security architecture & implementation
Requirements become practical technical decisions: identities and permissions, separate environments, secure interfaces, logging and recovery. Implementation is coordinated with your IT team and service providers.
Concrete use casesWhat this could look like
What this could look like
in practice.
Illustrative project scenarios show possible approaches. They are not documented customer references.
Bring structure to an established security setup.
The starting point
Security measures have developed over years. Documentation, recovery procedures and responsibilities are held by different people; a shared view of key risks is missing.
A possible approach
An inventory could bring together critical business processes, systems, providers and existing evidence. Risks are then assessed and measures planned with owners and review criteria.
Possible outcome
The aim is a reliable basis for security planning: visible gaps, justified priorities and agreed responsibilities rather than an unweighted list of measures.
Introduce an internal knowledge assistant with control.
The starting point
A department wants to search confidential documents with AI. It is unclear which data may be processed, who may view results and how incorrect answers will be handled.
A possible approach
A limited pilot could review data classes, access roles, provider terms and possible misuse. A usage concept defines permitted sources, human review and incident handling.
Possible outcome
The aim is a documented decision on appropriate usage boundaries. Technical and organizational prerequisites are clearly described and testable before wider approval.
Make security evidence part of daily work.
The starting point
Customers ask about information security. Some policies exist, but risks, regular reviews and implementation of agreed measures are recorded inconsistently.
A possible approach
An agreed ISMS project could clarify scope and connect existing workflows with risk management, responsibilities and evidence. Regular reviews are incorporated into established routines.
Possible outcome
The aim is a maintainable management system whose documented rules match actual practice. Any certification is planned separately with an appropriate independent body.
Security as an ongoing process
Connect technology, organization and evidence.
Information security becomes sustainable when protection needs, practical implementation and regular reviews work together.
01Protection needs
Which information and processes are particularly important to business operations?
02Responsibility
Who decides, who implements and who checks delivery?
03Measures
Which technical and organizational improvements address the identified risks?
04Evidence
How can responsible staff tell whether agreed measures actually work?
Schematic approach. Review scope and applicable requirements are assessed specifically for your business.
A transparent approachFrom the first conversation
From the first conversation
to a controlled outcome.
Each phase informs the next decision. Scope, responsibilities and acceptance are agreed before implementation.
- 01
Assess the starting point
We clarify goals and scope, review existing documents and speak with responsible staff. Systems and permitted assessment activities are defined in advance.
Possible deliverableDefined inventory with outstanding questions - 02
Prioritize risks
Findings are assessed by their possible impact on operations. Together, we identify appropriate measures and document the reasoning.
Possible deliverablePrioritized risk overview and action plan - 03
Implement measures
We support organizational and technical improvements within the agreed scope. Responsibilities, evidence and required changes are coordinated with the teams involved.
Possible deliverableCompleted work packages with clear responsibilities - 04
Review effectiveness
We use agreed criteria to check whether measures serve their purpose. Remaining gaps, changed circumstances and future reviews are recorded.
Possible deliverableReview results and improvement plan
Your starting point
Initial Security & Compliance Assessment
A structured starting point for businesses seeking clarity on required action. Together, we define the processes, systems and documents covered. Scope, participation and effort are agreed in advance.
- Overview of the assessed situation and key gaps
- Transparently prioritized areas for action
- Recommendations for next steps and specialist involvement
Software when it fits the need
Tools for your workflows.
Our own applications can complement delivery. Your requirements and actual interfaces are decisive; other suitable technologies are also considered.
 On request
Security & ComplianceMCP-enabled
NALVRA GOVERN
AI inventory and governance for a structured overview.
View product External website · new tab On request
Security & ComplianceMCP-enabled
NALVRA ERASE
Tools for data deletion and documented deletion workflows.
View product External website · new tab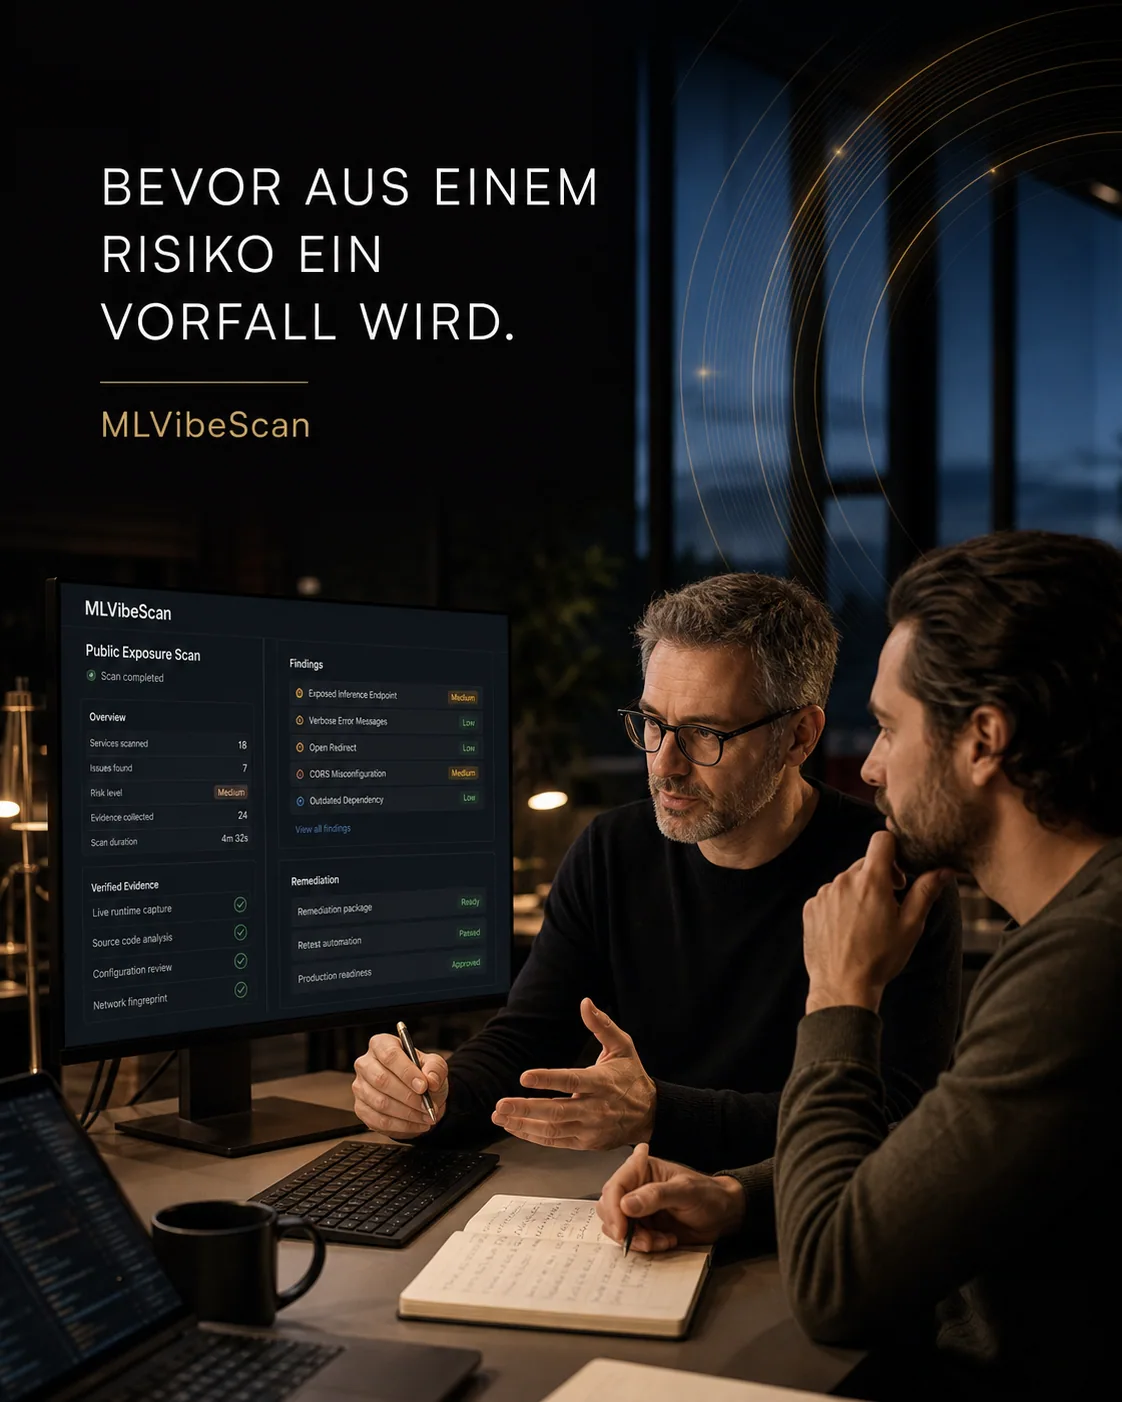 On request
Security & ComplianceMCP-enabled
NALVRA SCAN
Assessment tools and structured findings for web applications.
View product External website · new tabSee the connectionsAnother perspective
Another perspective
can be worthwhile.
Questions before the first step
Useful questions. Clear answers.
Is an AI project required?
No. Information security and compliance are independent consulting areas.
Will we receive ISO certification?
NALVRA supports preparation, structures and implementation. Certification is carried out by an appropriate independent body.
Can we start with a single security area?
Yes. A clearly limited area, such as permissions, AI use or recovery planning, can be a suitable starting point. Dependencies and assessment limitations are explicitly documented.
Will our internal teams and providers be involved?
Working with existing responsible staff is essential. Measures must be technically feasible and maintainable in operations. Access, roles and participation are agreed at the start; confidential information is processed only within the agreed framework.
Your project. Our next conversation.
A good next step starts with clarity.
Describe your situation. We will discuss goals, technical prerequisites and a suitable starting point.